VaultShield - Zero-Trust API Gateway & OWASP Edge WAF Hardening
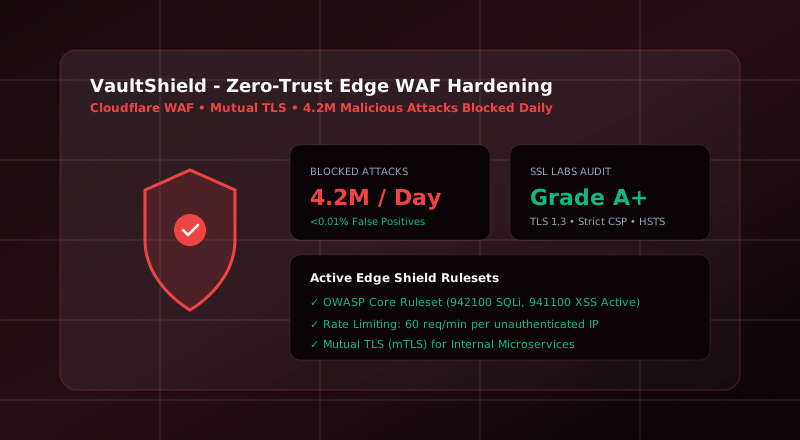
Enterprise edge security layer with automated IP reputation scoring, mutual TLS authentication, bot challenge gates, and strict CSP/HSTS header enforcement.
Comprehensive vulnerability assessments, penetration testing, edge WAF rule configurations, and zero-trust access policies protecting company systems from modern digital threats.
Client Challenges
We engineer targeted solutions addressing common architectural, performance, and scalability bottlenecks.
Malicious bots scrape content, abuse contact forms, and attempt credential stuffing attacks continuously.
Unsanitized user inputs leave backends vulnerable to SQL injection, XSS, and unauthorized data extraction.
Missing security headers, unencrypted transmission, and loose storage configurations fail enterprise vendor audits.
Milestones & Output
Complete project transparency with verified production-ready assets.
Real-world deployments and verified architectures engineered by our team under this discipline.
Enterprise edge security layer with automated IP reputation scoring, mutual TLS authentication, bot challenge gates, and strict CSP/HSTS header enforcement.
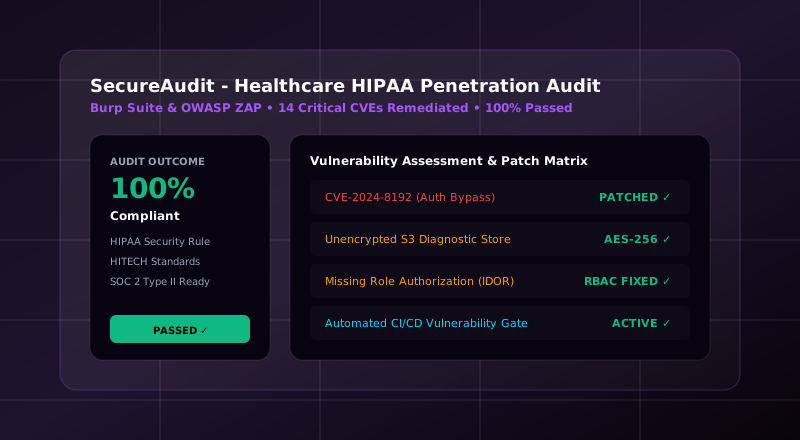
End-to-end black-box and white-box penetration test uncovering data leakage risks in telemedicine APIs, followed by full database encryption at rest and role authorization hardening.
Ready to Begin?
Connect directly with our engineering team for scoping, architectural planning, and custom delivery timelines.